Introduction
Infisical leverages a Key Management Service (KMS) to securely encrypt and decrypt secrets in your projects.Overview
Infisical’s KMS ensures the security of your project’s secrets through the following mechanisms:- Each project is assigned a unique workspace key, which is responsible for encrypting and decrypting secret values.
- The workspace key itself is encrypted using the project’s configured KMS.
- When secrets are requested, the workspace key is derived from the configured KMS. This key is then used to decrypt the secret values on-demand before sending them to the requesting client.
Configuration
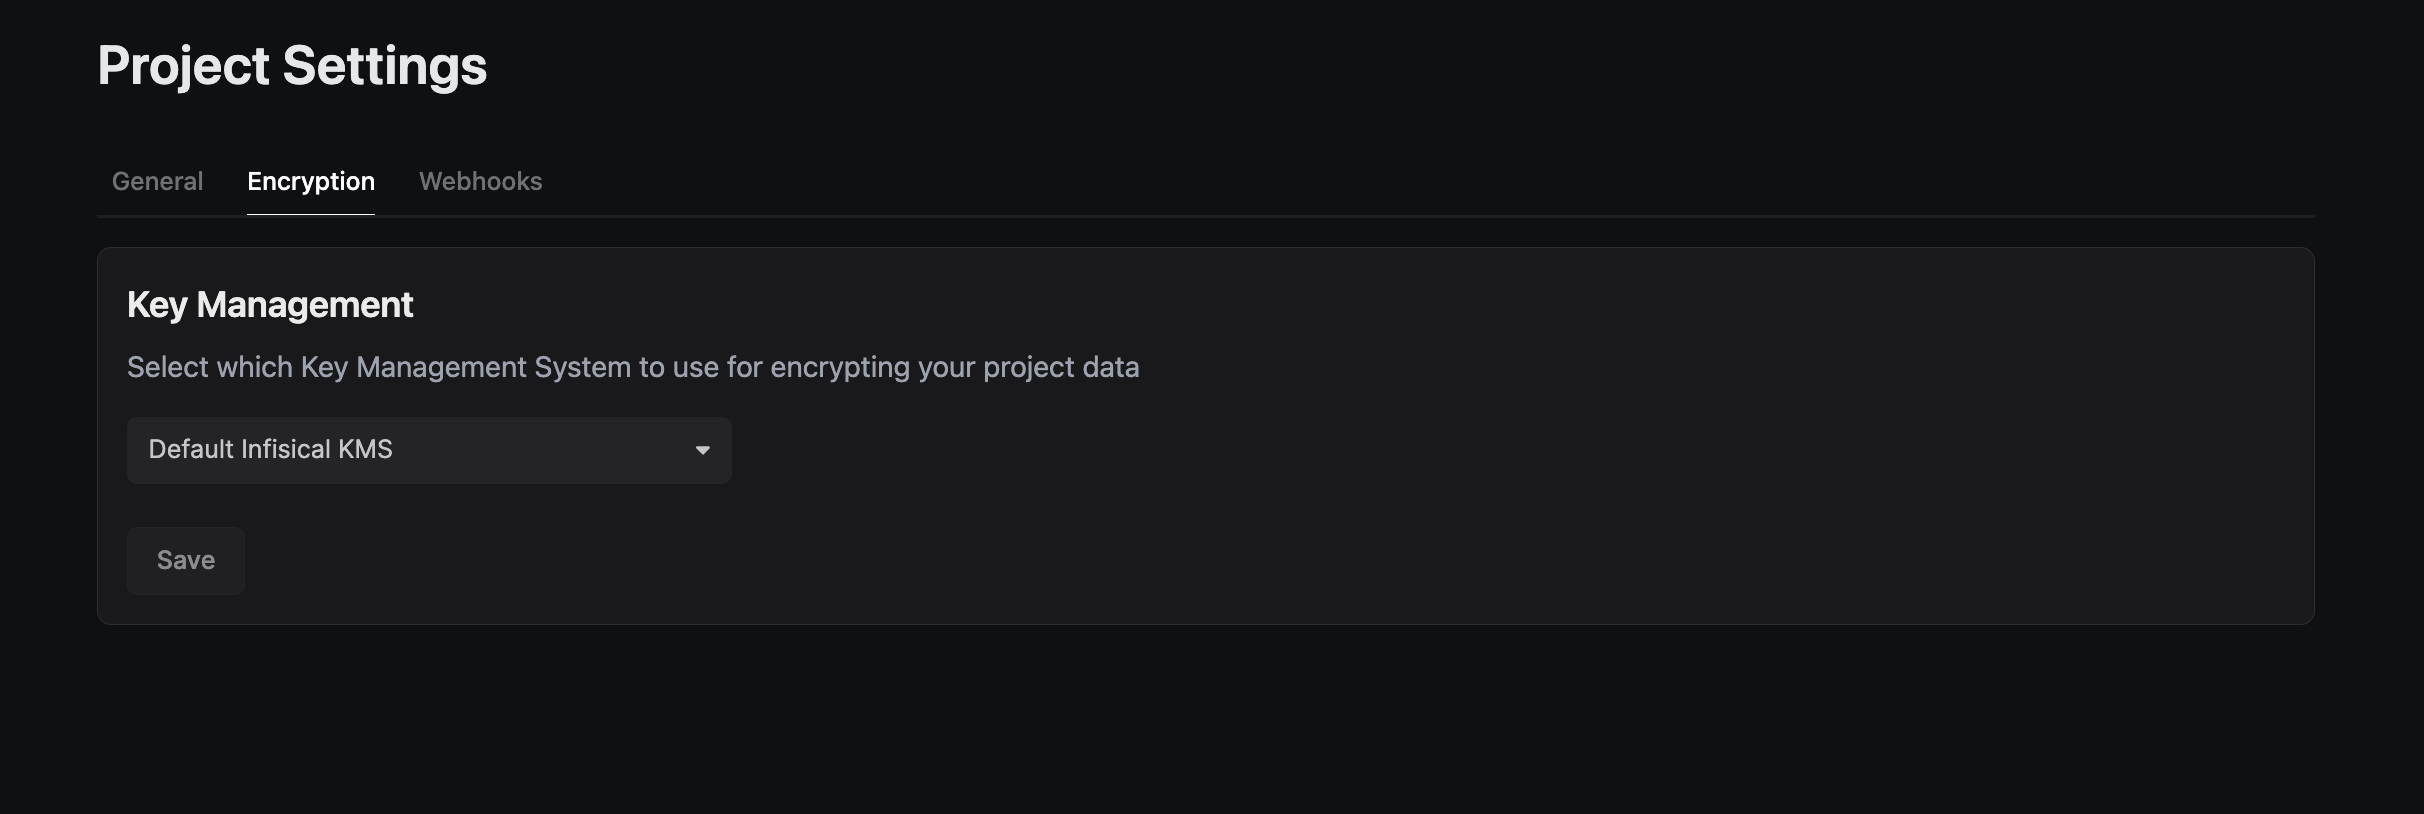
You can set the KMS for a new project while creating it: expand Advanced Settings in the create project dialog and pick from the KMS dropdown.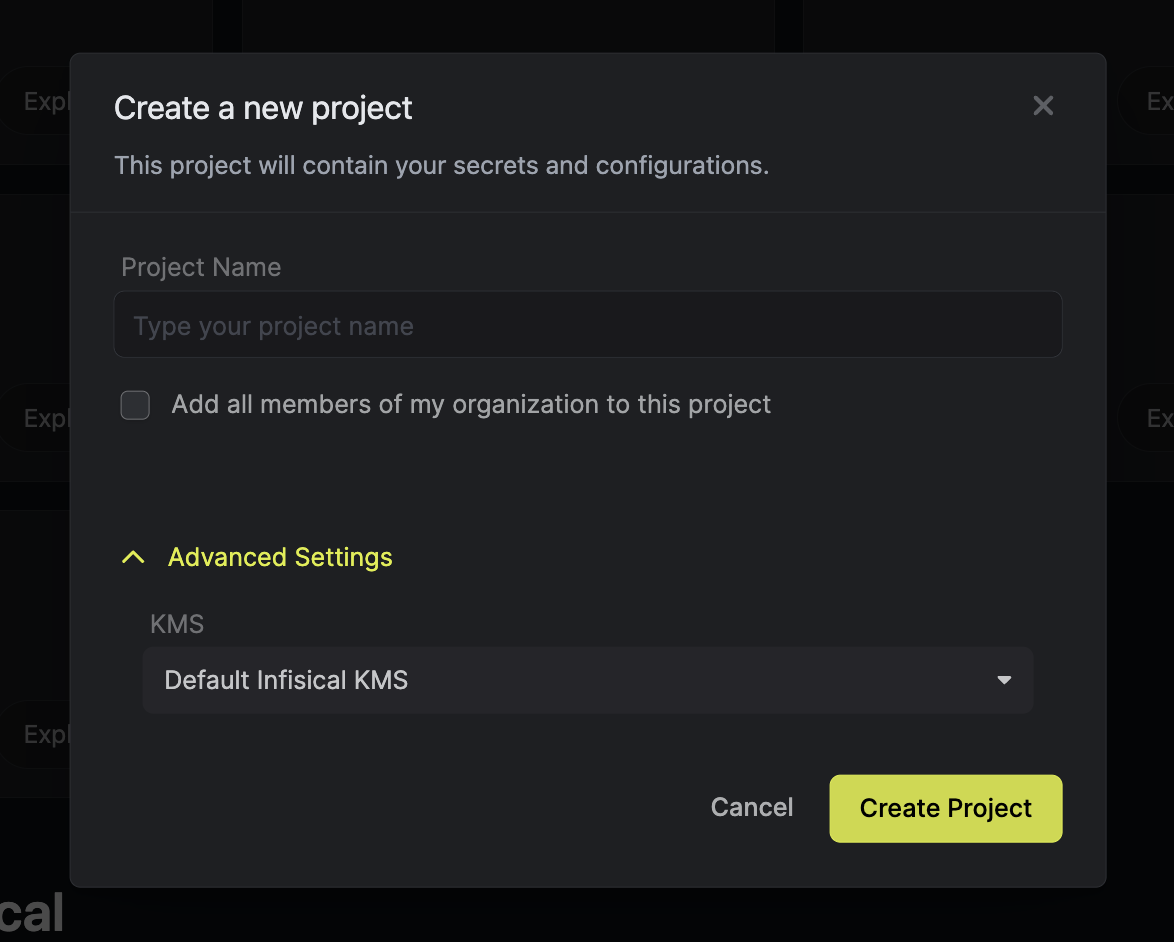 For an existing project, go to the project’s Settings and select Encryption.